The problem
- Context
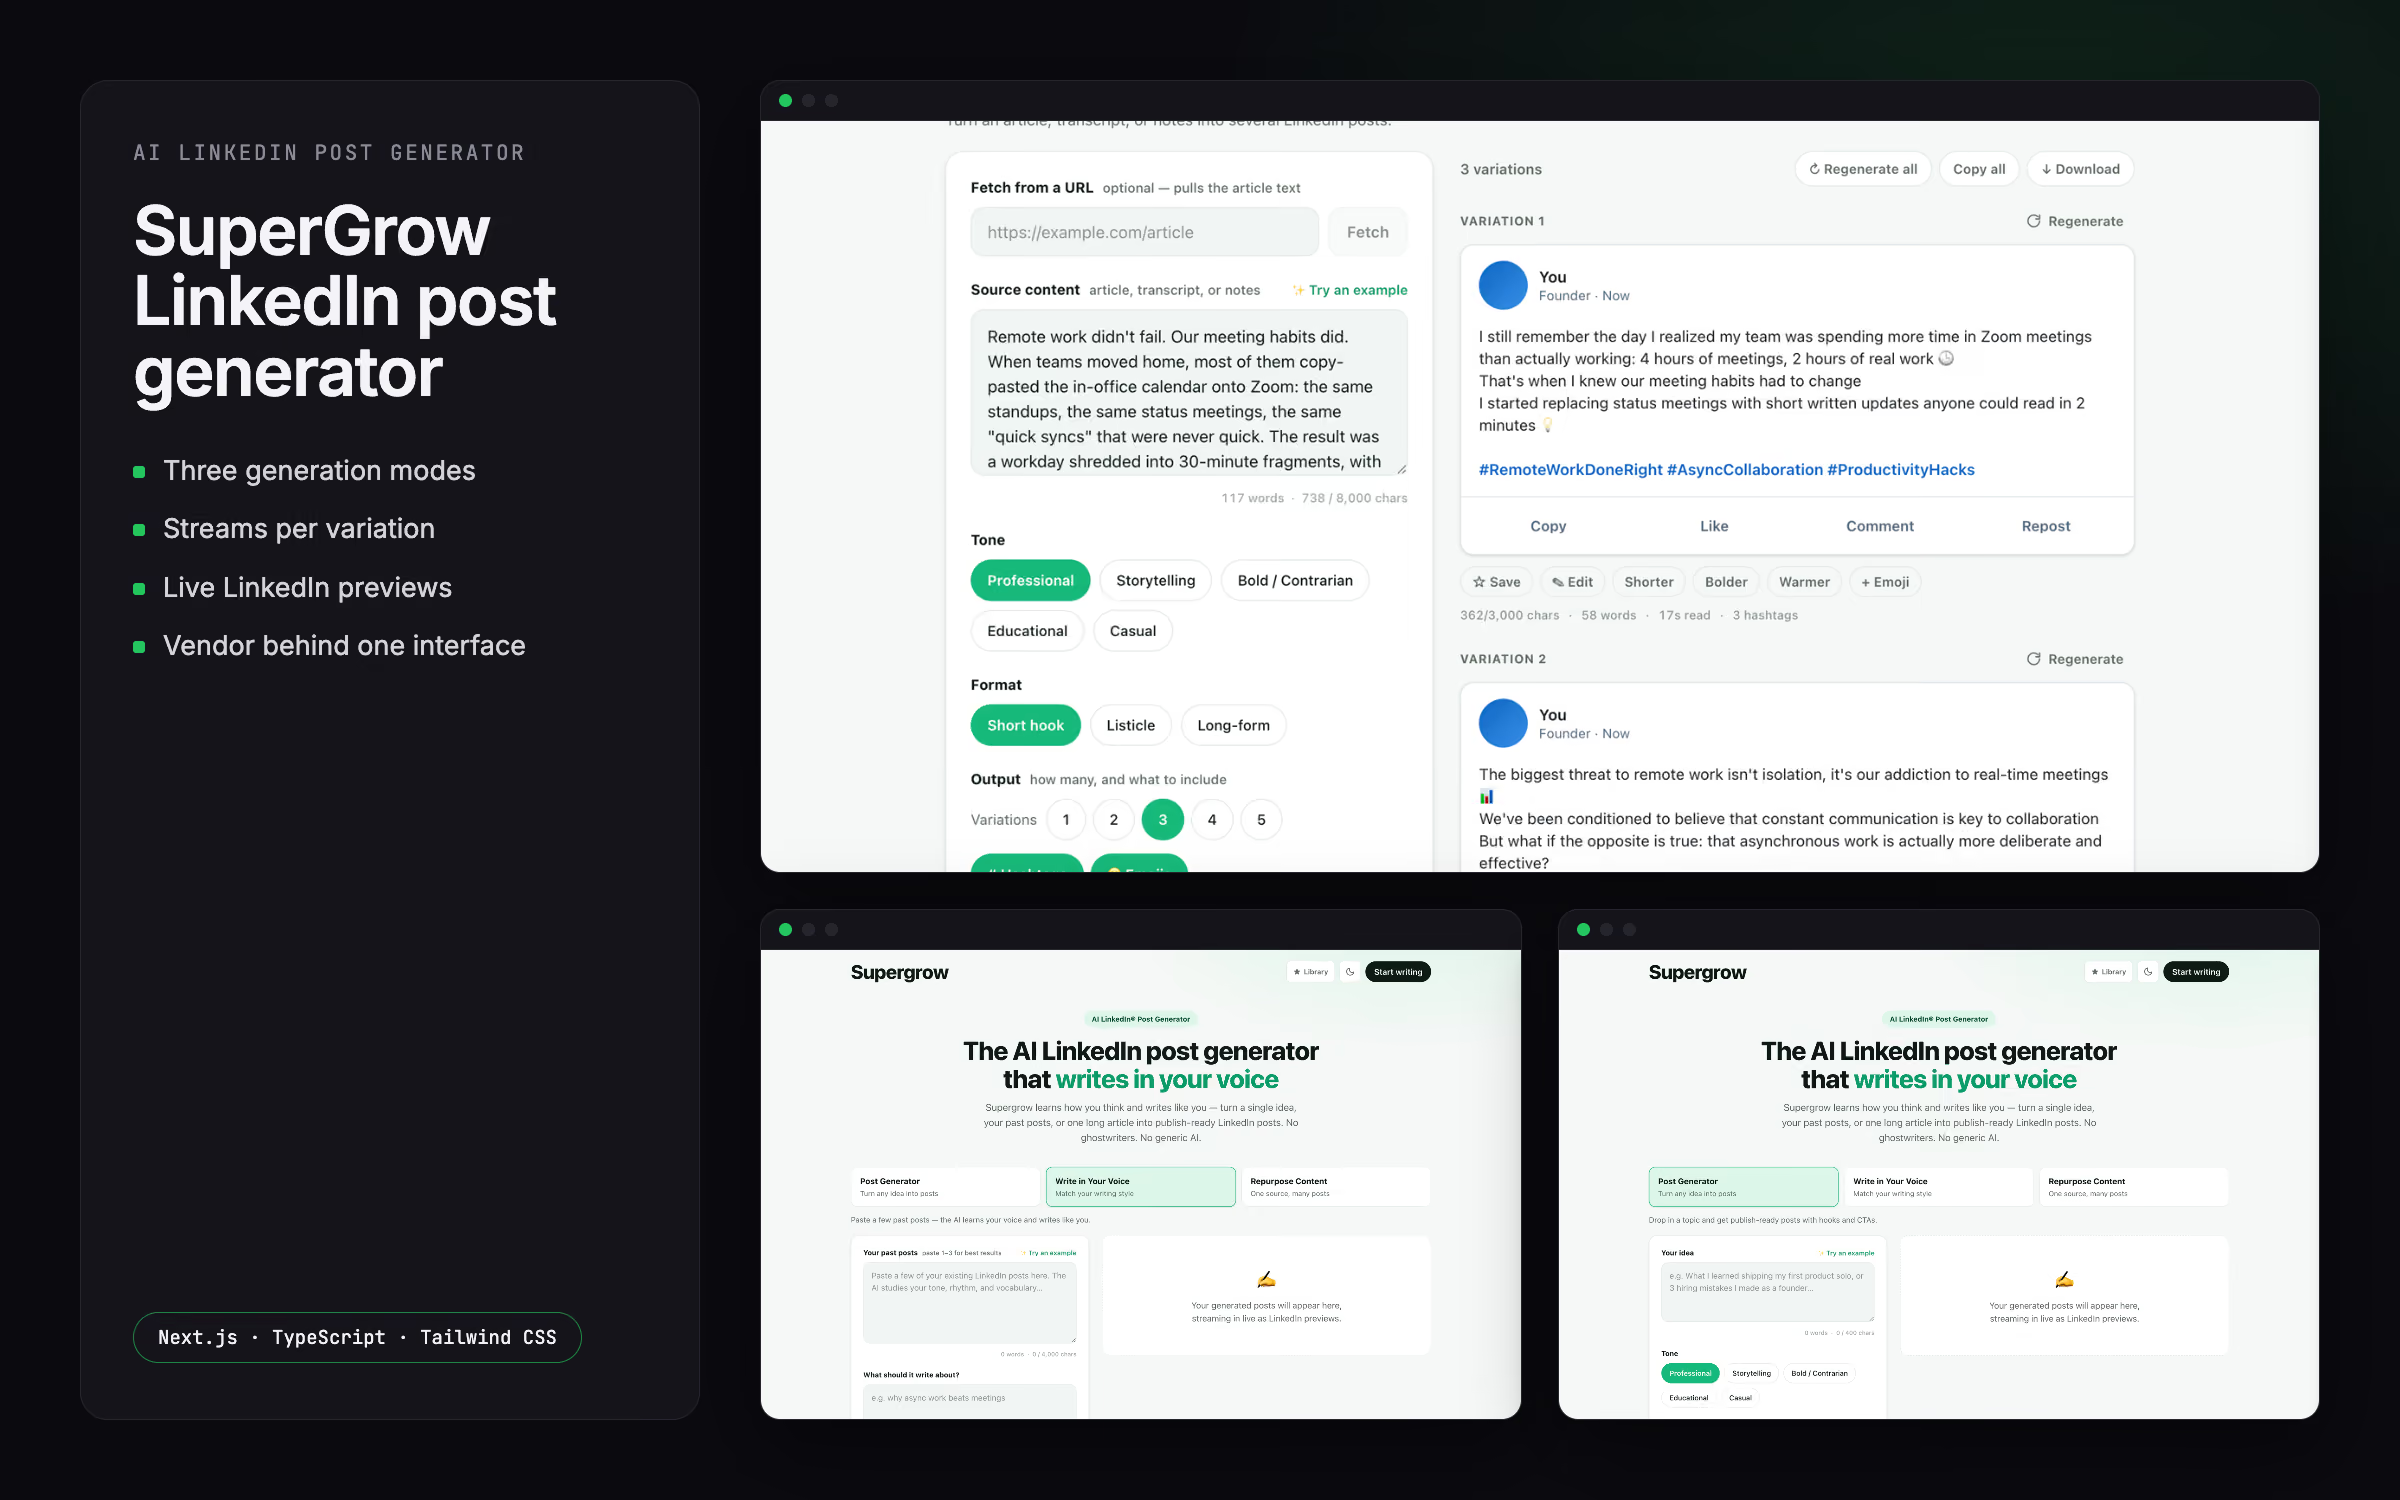
- A writer starts from a bare topic, a few of their own past posts, or an article they want to repurpose, and gets one to five LinkedIn-ready posts that stream in as live LinkedIn previews.
- Constraints
- It is only useful if it is fast enough to iterate on and the output looks like what will be published. The demo runs behind one shared login, and the repurpose mode fetches web pages that visitors supply, which is a classic way into a server's internal network. No heavyweight AI SDK was wanted.
- What was at stake
- Slow or badly formatted output kills iteration. A forgeable session or unthrottled login would open the demo to anyone, a naive server-side fetch would let a visitor reach internal addresses, and leaking raw provider errors would expose how the system is built.
What I built
Generation
One provider interface
The route asks an interface for a model rather than naming a vendor, and the current provider is called directly over its streaming API with no SDK. Swapping vendors changes one file.
Three modes, one prompt builder
Topic, write-in-your-voice and repurpose share one prompt builder. Voice mode deliberately drops the tone setting so the writer's own sample wins, and repurpose builds a post around the single most interesting idea rather than summarising.
Variations that actually differ
Each of the one to five variations is given a different angle, and any single card can be regenerated or remixed (shorter, bolder, warmer) without re-running the rest.
Streaming per card
Each post streams in as it is written. Problems are reported before streaming starts, and a failure midway keeps what has already arrived.
Security
Safe fetching of visitor URLs
Every redirect is followed by hand and re-checked; internal names, raw IP addresses and anything resolving to a private or cloud-metadata address are refused. Size, redirects, content type and time are all capped, and when a site blocks bots the user is asked to paste the text instead.
A gate that fails closed
Sessions are HMAC-signed HTTP-only cookies; credentials are compared in constant time with both fields always checked; five failed attempts lock an address out for three hours. With no credentials configured, nobody gets in.
Inputs capped, errors kept private
Every input is validated and length-capped so a crafted request cannot inflate the prompt. Rate limits get a friendly message; other provider errors are logged on the server and shown to the user only as 'temporarily unavailable'.
Previews that match LinkedIn
The 'see more' fold and limits
Each preview cuts at LinkedIn's fold (three lines or 210 characters, at a word boundary) and shows characters, words and read time against the 3,000-character limit. Hashtags are cleaned into valid tags.
Tested where it matters
Unit tests cover sign-in, post parsing, prompt building, rate limiting and the URL safety checks.
Tell me what you’re building and where it’s stuck.
I’ll tell you the cleanest path forward, including if it’s “don’t build that.”
Or write tocontact@alihassan.dev